Denmark CPR Breach Traced to Vendor Account Using 123456 Password
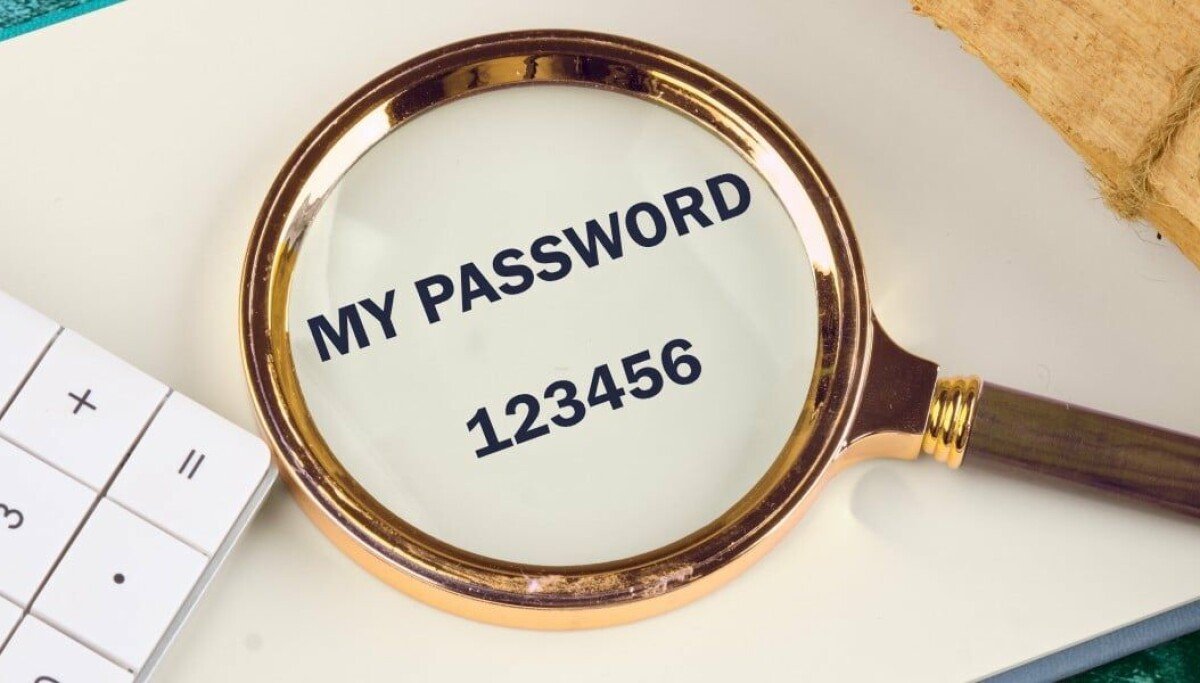
The Denmark CPR breach has exposed personal information belonging to 8.8 million individuals after threat actors compromised an IT vendor’s system account secured by the password “123456.” Danish newspaper Politiken reported that the person claiming responsibility accessed the Central Register of Persons through Pays ApS, a Funen-based company with authorized access to validate business customer records. Furthermore, at least three company accounts, including one with administrative privileges, shared the identical weak credential.
Government officials confirmed the intrusion on October 5, though they initially declined to name the compromised vendor. Managing director Sophie Laursen acknowledged Pays ApS as the affected entity on October 9. Meanwhile, the company’s website has been taken offline, and requests for comment regarding the password allegations have gone unanswered.
Attacker Conducted 14 Million Automated Searches Over Ten Days
According to documents obtained by broadcaster TV 2, the unauthorized access began on September 10 and continued until September 20. During this period, the intruder executed approximately 14 million automated queries against the CPR database. Consequently, the register’s roughly 11 million records — including entries for deceased persons and former residents — were potentially viewable. However, the individual behind the activity told Politiken they had no plans to sell or publish the harvested data.
Detection occurred on October 2, twelve days after the final search activity. A ministry staffer noticed an invoice reflecting unusually high system usage from Pays ApS, prompting an internal review. Subsequently, the Danish data protection authority Datatilsynet received notification on October 4, followed by public disclosure the next day.
Security Failures Highlight Systemic Credential Hygiene Gaps
This incident underscores persistent failures in basic credential management across critical infrastructure supply chains. The use of “123456” — consistently ranked among the most common passwords globally — on an administrator account with access to a national identity register represents a severe governance lapse. Additionally, the reuse of this credential across multiple accounts amplified the blast radius considerably.
Security experts emphasize that multi-factor authentication and privileged access monitoring could have prevented or limited the compromise. The Danish government has not yet responded to questions about the alleged password failures or whether broader audits of CPR-access vendors are planned. For organizations managing sensitive data access, the UK National Cyber Security Centre provides updated guidance on credential policies.
Ultimately, the Denmark CPR breach serves as a stark reminder that sophisticated defenses cannot compensate for fundamental hygiene failures. As investigations continue, affected individuals should monitor for potential identity misuse and consider credit monitoring services where available.
Denmark Cpr Breach Market Impact and Industry Significance
The introduction of Denmark Cpr Breach represents a pivotal shift in modern technological adoption across enterprise and consumer sectors alike. Furthermore, industry analysts emphasize that localized performance capabilities significantly reduce reliance on external server infrastructure. Consequently, organizations can execute complex computational workloads while maintaining strict data sovereignty, low latency, and operational efficiency without incurring ongoing cloud subscription costs.
Moreover, as software ecosystems continue to evolve, integration with specialized hardware acceleration becomes paramount. Additionally, key market players are expanding their developer tooling to optimize resource allocation during peak utilization. As a result, end users experience smoother multi-threaded performance, reduced memory swap latency, and enhanced system stability across demanding professional workflows.
Performance Benchmarks and Practical Denmark Cpr Breach Scenarios
In real-world deployment scenarios, evaluating sustained throughput and thermal efficiency is essential for technical decision-makers. Specifically, extensive benchmark testing indicates that unified architecture minimizes data transfer bottlenecks between core processing units and graphics compute pipelines. Therefore, demanding tasks operate with minimal compute overhead.
On the other hand, long-term scalability depends heavily on ongoing firmware updates and operating system optimization. Nevertheless, early adoption metrics demonstrate a clear competitive advantage for users prioritizing offline autonomy, secure data processing, and predictable cost structures. Ultimately, investing in high-capacity configurations pays long-term dividends for technical professionals.
Ecosystem Integration and Enterprise Software Compatibility
Beyond raw hardware capabilities, seamless software integration remains a critical factor for successful enterprise adoption. Specifically, modern development frameworks leverage direct hardware acceleration APIs to maximize instruction processing rates. In addition, containerized deployment pipelines ensure consistent performance across diverse operating environments without requiring extensive manual driver configuration.
Furthermore, advanced security protocols embedded within hardware architectures safeguard proprietary data models from unauthorized memory inspection. Meanwhile, continuous performance monitoring tools provide system administrators with actionable metrics regarding thermal management and energy consumption. Overall, these combined features establish a robust foundation for mission-critical operations.