Government Services Taken Offline Following Critical PHP Security Flaw
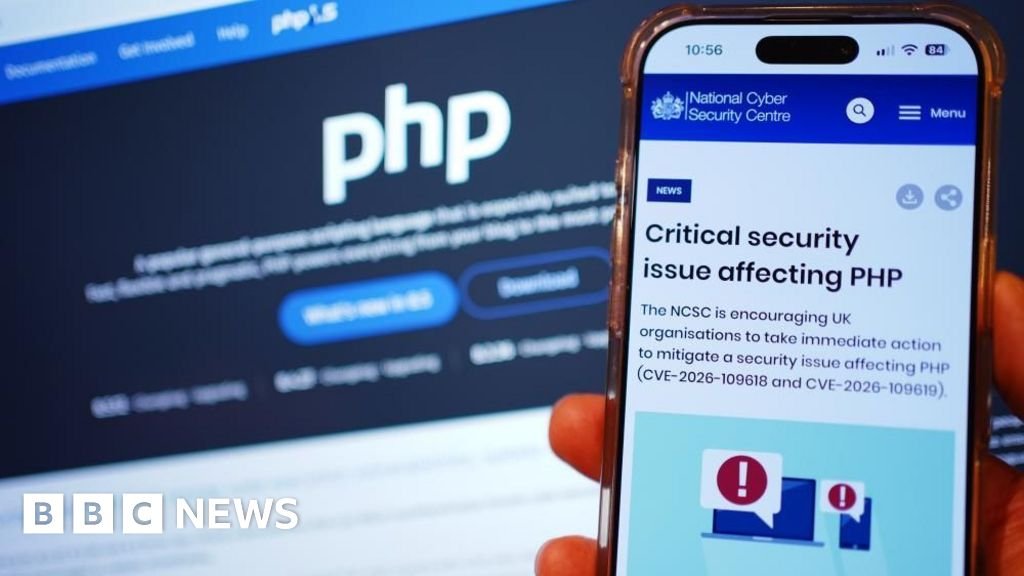
Dozens of government web services went dark this week as IT administrators scrambled to patch a dangerous PHP security flaw affecting web servers globally. Although no immediate breaches or successful attacks have been formally verified yet, the UK government proactively took numerous systems offline to prevent unauthorized access while emergency security updates were applied across the digital infrastructure.
The underlying issue stems from vulnerabilities discovered within the back-end language that has powered a significant portion of the internet for decades. Because millions of commercial websites rely on this technology, security experts warn that the true impact of the incident may take weeks or even months to fully materialize across the broader digital landscape.
Php Security Flaw: Why This Vulnerability Sparked a Global Scramble
Tech leaders and cybersecurity researchers have labeled the situation unprecedented in modern web management. Unlike isolated software bugs, a core server-side language vulnerability affects the foundational layer where web applications process user requests, database queries, and dynamic page generation.
- Over 30 government digital services experienced temporary outages.
- Public-facing critical infrastructure remained shielded from major disruptions.
- Administrators worldwide rushed to deploy emergency software patches.
- Small businesses reported unexpected delays in digital filing systems.
In terms of Php Security Flaw, Although major public portals managed to avoid widespread disruption, smaller commercial operations felt the pinch immediately. Local service providers, such as regional vehicle testing garages, found themselves unable to process digital certificates or upload regulatory paperwork to central networks, forcing staff to temporarily revert to manual paper records.
How This Compares to Past Software Crises
Industry analysts note that vulnerabilities in foundational web languages carry a much heavier risk profile than standard application bugs. While a faulty mobile app update usually requires a simple client-side patch, server-side code execution risks can expose sensitive backend databases to remote attackers.
Compared to previous isolated exploits, this incident highlights the fragile interdependencies underpinning modern digital infrastructure. Because countless platforms rely on legacy codebases, patching requires meticulous testing to avoid breaking existing enterprise workflows while simultaneously blocking potential exploits.
What This Means for Developers Going Forward
In terms of Php Security Flaw, Moving ahead, cybersecurity authorities emphasize that routine maintenance and rapid patch deployment must become standard operating procedure for both private enterprises and public institutions. Organizations relying on legacy frameworks can no longer afford to delay software updates.
As systems slowly return online following extensive security audits, the episode serves as a sharp reminder of the hidden vulnerabilities lurking within everyday digital architecture. For further details on software resilience, check out insights from the National Cyber Security Centre.